
TIBER-BE Insights

The TIBER-EU framework is designed to help organisations improve their Cyber resiliency. It has multiple stages: initiation (scoping, procurement, planning), threat intelligence, penetration testing (red teaming), purple teaming (attack replays, additional untested control tests, variances in attack methodologies working alongside the Blue team), and closure (reporting, remediation plans, attestation). As a framework, TIBER can be […]
Cyber Threats & The Boardroom
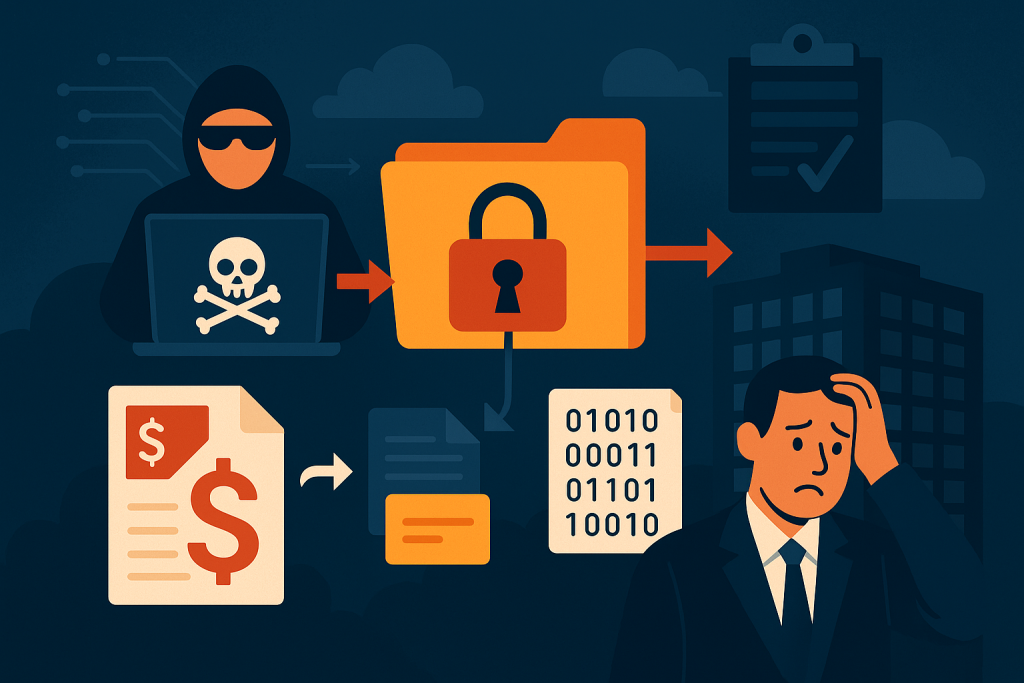
In cybersecurity, the prevalent and growing threat from criminals is ransomware operations. This is where a threat actor manages to establish a foothold into an organisation, will try to position themselves to gain control of the organisation’s data, will often steal some or all of that data, and then encrypt as much of it as […]
Passwords
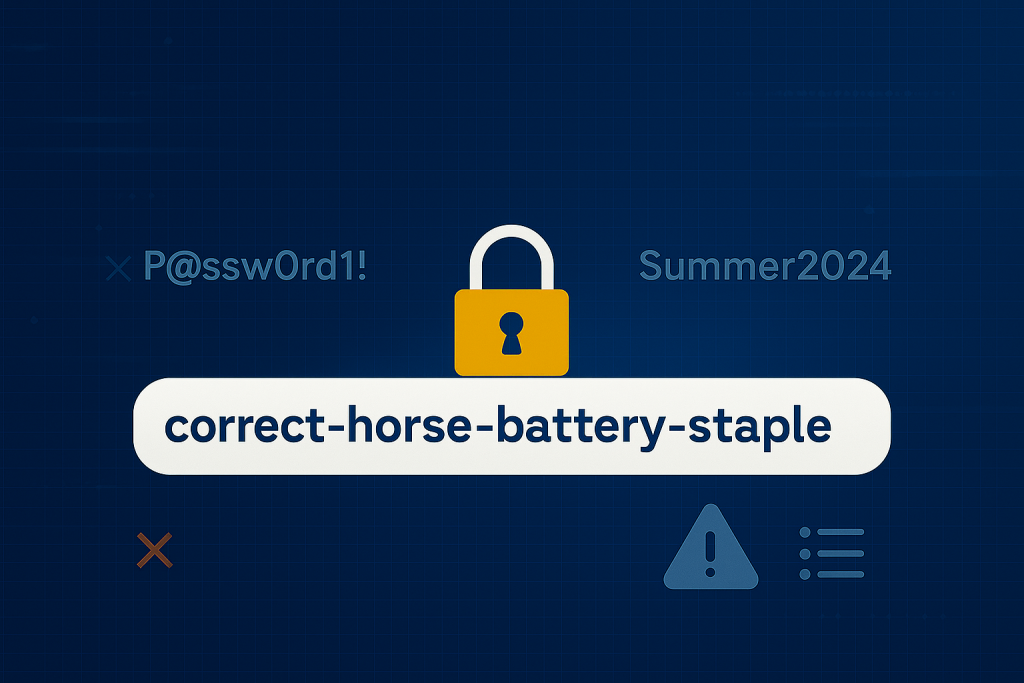
NIST, like the NCSC have updated their password guidance. It is now no longer advisable to set them to be random strings of nonsensical letters, numbers and symbols. The focus is now on password length, by stringing together multiple words. Inclusion of uppercase, and symbols or numbers is still helpful, to make them even harder […]
The Quantum Spectre at the Banquet
Quantum is tipped to be the next big thing in computers, and it has been for some time – in fact it was first conceived in the 1980s; however the issue was not really considered until the mid-1990s. Now, it’s seen as a potential game changer in the world of cryptography, where the world’s secrets […]
Prism Infosec Appoints Andrew Turner as Chief Commercial Officer
Cybersecurity consultancy Prism Infosec, with offices in Cheltenham and Liverpool, is pleased to announce the appointment of Andrew Turner as its new Chief Commercial Officer (CCO). Andrew brings a wealth of experience in cybersecurity and commercial leadership. He holds a degree in Computer Information Systems Design from Kingston University and most recently served as Vice President of Sales, EMEA at […]
The Cyber Security and Resilience Bill – April 2025
In the King’s Speech it was announced that further details would follow about the CSR Bill, and it looks like we now have the confirmed and proposed measures: Cyber Security and Resilience Bill: policy statement – GOV.UK These have been proposed by both MPs and the Department for Science, Innovation and Technology (DSIT) and backed […]
Prism Infosec Launches Vulnerability Remediation Service
Prism Infosec is proud to announce the launch of a remediation service line that will enable organisations to promptly implement effective fixes for vulnerabilities identified during engagements. The remediations service connects organisations with Prism Infosec’s team of IT and security experts to deliver tailored solutions that address vulnerabilities while ensuring compliance with industry standards and […]
Prism Infosec Achieves CBEST Accreditation

Prism Infosec, an established CHECK accredited Penetration Testing company, is pleased to announce that we have achieved accreditation status as a Threat-Led Penetration Testing (TLPT) provider under the CBEST scheme, the Bank of England’s rigorous regulator-led scheme for improving the cyber resiliency of the UK’s financial services, supported by CREST. This follows our recent accreditation […]
DORA – What Does it Mean for Business?
The Digital Operational Resilience Act (DORA) is a European legislative act that will be applied from the 17th of January 2025 and will apply to all financial entities (except for microenterprises). It is designed to strengthen European financial entities against cyber-attacks and ICT (Information and Communication Technology) disruptions. The full original text (in English) can […]
Capitalising on the Investment of a Red Team Engagement

Cybersecurity red teams are designed to evaluate an organisation’s ability to detect and respond to cybersecurity threats. They are modelled on real life breaches, giving an organisation an opportunity to determine if they have the resiliency to withstand a similar breach. No two breaches are entirely alike, as each organisation’s organic and planned growth of […]
